
Proxy Authentication Explained: Username, Password and IP Whitelisting
You finally found a proxy that looks fast. Then the setup page asks for something you did not expect: a username and a password, or a dashboard setting called IP whitelisting, or nothing at all. Pick the wrong one and nothing works, and the error message will not tell you why.
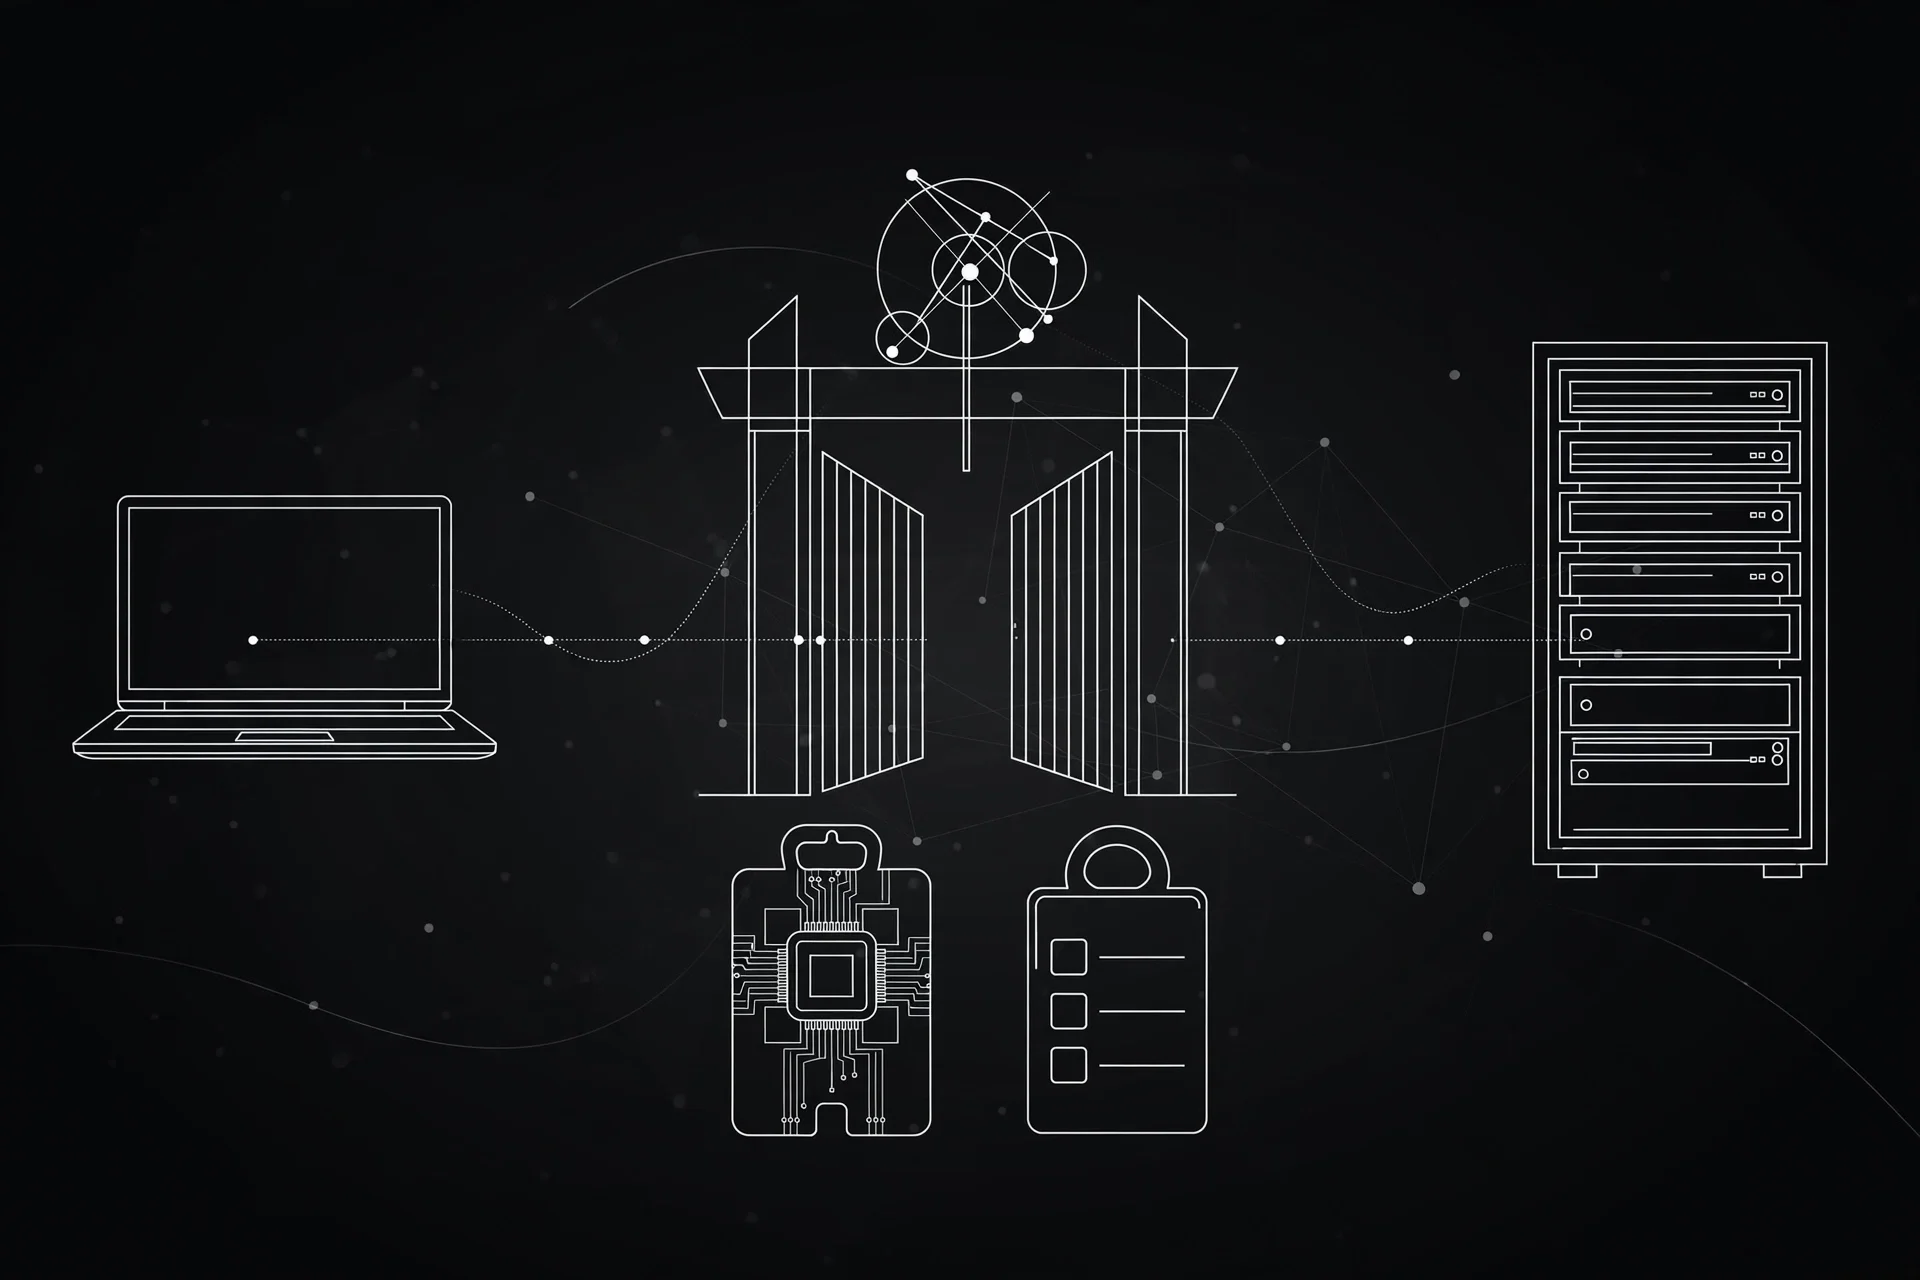
The real problem: two gates, and no sign on either one
Proxy authentication is just the proxy asking, "Are you allowed to use me?" Paid proxies need an answer, because the provider is selling access. The trouble is that providers answer it in two completely different ways, and most setup guides describe only one.
When I tested this for a friend who runs a small price-checking script, his setup failed for a week. His provider used IP whitelisting, and he kept typing a username and password the provider had never issued. The moment he added his server IP to the dashboard, the same script worked on the first try. Find out which gate yours has before you touch anything else.
Here is my blunt take: most guides explain both methods, then hand you a comparison table and leave. A table does not fix your 407 error at midnight.
The two gates, plainly explained
Gate 1: username and password
With this method, every request carries a login. The proxy checks it, then forwards the request. It works from anywhere: home, mobile data, or a server abroad.
You will usually see it written as one address: http://user_4821:[email protected]:8080. That packs the host, port, and login together. The numbers are examples only, from the documentation range, not a real proxy.
This method is the flexible one. It also has one sharp edge: the password travels with your requests. In the common Basic scheme it is base64 encoded, and base64 is encoding, not encryption. Anyone who can read the traffic can reverse it in seconds. So only use it over HTTPS destinations or a SOCKS5 setup you trust, and never paste the full string into a public forum, a screenshot, or a shared document.
Gate 2: IP whitelisting
With this method, there is no login at all. You tell the provider your public IP address, the provider adds it to an approved list, and the proxy lets through any request from that address. Requests from anywhere else get refused, even with a perfect password, because there is no password to check.
That sounds simpler, and for a fixed server it is. No secrets to store, nothing to leak. The catch is the word fixed. Your home IP can change when your router restarts, and mobile data changes constantly. A laptop that worked in the office will fail at a coffee shop, because that IP is not on the list. The proxy is not broken. Your address changed.
One more trap: the IP you whitelist must be your public IP, the one the internet sees, not the 192.168 address your router gives your laptop at home. Open our What Is My IP tool from the exact device or server that will use the proxy, and whitelist the address it shows.
Prefer watching? This walkthrough explains the 407 proxy authentication error and how to fix it.
Which gate fits your setup?
Simple rule: if your IP stays the same for weeks, whitelisting is cleaner. That covers a VPS, a home server, or an office with a static connection. If your IP moves, or several people in different places share the proxy, use username and password. That covers laptops, phones, and remote teams. For a team, give each person their own login so you can revoke one without breaking everyone else.
Set up a username and password without leaking it
In a browser, the first connection should prompt you for the login. Save it only on a device you control, never on a shared machine.
In a script, the safest pattern is an environment variable, not a password typed into the code. Read the proxy URL from the environment and never commit the real string to your repository. With curl, pass the login with the --proxy-user flag rather than baking it into a shared shell script. If a password contains an @ sign, a colon, or a dollar sign, URL-encode it first, because an unencoded @ splits the address in the wrong place.
Fix the 407 error, and the failures that look like it
HTTP 407 means the proxy wants authentication it did not get, or got wrong. MDN defines 407 as a request that failed because it lacks valid credentials for the proxy server between you and the site. The proxy is asking, not the website, so changing the website address will never fix it.
- 407 with a login: re-copy the login from the dashboard, check for a trailing space, and re-encode special characters. Test with one curl request before touching app code.
- 407 with whitelisting: check your current public IP with the What Is My IP tool. If it differs from the whitelisted one, add the new IP.
- Browser works, script fails: the browser is probably using saved credentials the script lacks. Give the script the same login through an environment variable.
- No 407, just a silent failure: check the proxy itself with our Proxy Checker. A dead proxy and a wrong login look identical from the outside.
The ProxyNest difference: our free proxies need no login at all
Here is the part that surprises people who arrive from a paid provider. Every proxy on the ProxyNest proxy list is public, and public proxies do not use either gate. You copy the IP and port, paste them in, and go. No account, no username, no password, no whitelist. If a site calling itself free asks you to log in to a proxy, treat that as a warning sign. A login on a supposedly free public proxy is how credentials get harvested.
That freedom comes with a trade. Public proxies are shared, unstable, and sometimes slow, and they are not a safe place for banking or private accounts. Our honest guide to free proxy safety says that plainly. Use ProxyNest to learn, test, or browse casually, or pick a proxy by country from the locations page. When a job needs a login or a stable IP, a paid authenticated proxy earns its price.
Your 60-second checklist
- Find out which gate you were given: login, whitelist, or none.
- For whitelisting, whitelist the public IP shown by the IP tool, from the device that will use the proxy.
- For a login, copy it fresh from the dashboard, encode special characters, and store it in an environment variable.
- Test once, confirm the exit IP, and only then point your real workload at the proxy.
- When it breaks later, check the IP or password first.
Authentication is not the interesting part of proxies, and that is exactly why it wastes so much time. Get the gate right once, write it down, and you will not debug this failure for a week again.
Comments
Loading comments…
Leave a comment