
Is My VPN Leaking? How to Test for IP, DNS and WebRTC Leaks
Your VPN app says "Connected." The little key icon sits in your status bar. Everything looks fine. But here is the uncomfortable question: is your real IP actually hidden, or is it quietly slipping out through a side door? Leaks happen more often than people think, and the fix usually takes minutes.
What does a "VPN leak" even mean?
When your VPN is on, all your traffic should flow through the VPN's server. Websites, apps and snoopers should only see the VPN's IP address. A leak is any moment that plan breaks down: your real IP, your real location, or your browsing requests escape outside the tunnel.
To the website on the other end, you look unprotected. And the scary part? Everything looks normal on your screen. The app still says connected. No error pops up. You would never know unless you actually checked.
Concrete example. You are in Lahore, using a VPN server in Amsterdam. A leak means some site can still tell you are actually in Lahore. Your stream stays geo-blocked, your ISP still sees where you go, and you paid for a service that is not doing its one job.
The three leaks that actually matter
There are three classic ways this happens. Once you know them, testing takes about a minute.
1. IP leak, the big one
This is the simplest failure. Your device just is not routing traffic through the VPN at all. Maybe the VPN app crashed in the background. Maybe your phone reconnected to Wi-Fi and the tunnel never came back up. You run a test and your real IP stares back at you.
Quick sanity check you can do yourself: open our What Is My IP tool while disconnected and note the address. Connect your VPN, wait a few seconds, check again. Different? Good. Same? You have a leak.
2. DNS leak, the most common
Every time you type a website address, your device asks a DNS server to translate it into an IP. With a VPN on, that question should go through the tunnel to the VPN's own DNS servers. But many setups, especially on Windows and some routers, keep asking your ISP's DNS server instead.
Your ISP cannot see the page content, but it can see every single site you ask about. You visit three news sites through your VPN; your ISP's logs still show you asking for those exact sites. That is a DNS leak, and it is the one most people have without knowing.
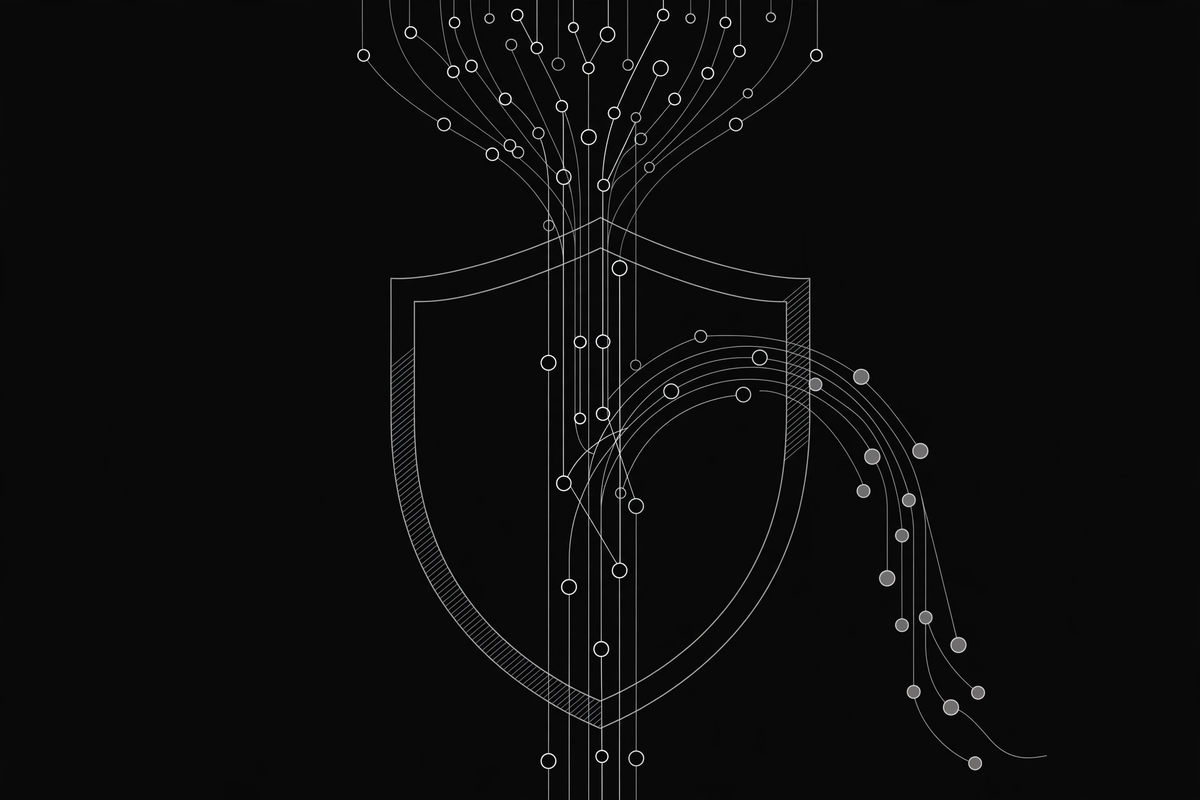
3. WebRTC leak, the sneaky browser one
WebRTC is a browser feature that lets sites do video calls and file sharing right in the page. To make that work, your browser quietly discovers your real local and public IP addresses, and any website can ask for them with a bit of JavaScript. No permission prompt. No warning.
This one is famous for biting people who did everything right: VPN on, kill switch on, but Chrome or Firefox hands their real IP to any site that asks. If you want the technical background, Wikipedia's WebRTC article explains how the protocol works.
The practical fallout? A streaming service can still geo-block you even with your VPN connected. That "not available in your country" message, while the app insists you are in Amsterdam. Annoying, and completely fixable.
How to test for leaks in 30 seconds
Enough theory. Here is the actual test, step by step:
- Disconnect your VPN. Open our VPN Leak Test tool. Write down the IP address it shows. That is your real one.
- Connect your VPN to any server. Give it a few seconds for the tunnel to settle.
- Hit retest on the tool. Now read the results:
- IP address: should be the VPN server's IP, not the one you wrote down.
- Location: should show the VPN server's country, not yours.
- DNS servers: should belong to your VPN provider, not your ISP.
- If any of those show your real details, you have a leak.
That is the whole test. It works the same way for proxies, by the way: connect a proxy from the proxy list, then check whether the tool shows the proxy's IP or yours. We cover that workflow in how to check any proxy in seconds.
Found a leak? Here is how to fix it
Do not panic. Most leaks come from settings, not from a broken VPN.
- Turn on the kill switch. Almost every decent VPN app has one, buried in settings under names like "kill switch," "network lock," or "auto-connect." It blocks all traffic if the tunnel drops. If yours does not have one, that is a red flag about the VPN itself.
- Fix your DNS. Many VPN apps let you force their own DNS servers or set a custom one. Do not leave it on "automatic" if automatic means your ISP.
- Tame WebRTC. In Firefox you can disable it in about:config (the media.peerconnection.enabled setting). In Chrome it is harder, so a WebRTC-blocking extension is the practical route.
- Update the app. Seriously. Old VPN clients have known leak bugs that newer versions fixed.
- Retest after every change. One test is not a one-time thing. Run the check again after updates, after switching servers, and especially after your device wakes from sleep.
Sometimes it is not your VPN's fault
Two honest caveats. First, a "VPN" that is actually just a browser extension only protects browser traffic. Your apps leak happily beside it. If that is your setup, know its limits.
Second, IPv6. If your VPN only handles IPv4 and your network pushes IPv6, your real address can walk right out the IPv6 door. Good VPN apps tunnel or disable IPv6 by default; cheap ones do not. If the leak test shows an IPv6 address you recognize, that is your culprit. More background on what your address actually reveals is in our IP address guide.
Test it now, while you are thinking about it
A green "Connected" badge is a promise, not proof. The test takes less time than reading this article took. Run it, and if it comes back clean, you can actually relax.
And here is the honest bit: this applies to proxies too, not just VPNs. Free proxies are leakier by nature, which is why we wrote the full uncomfortable truth in Are Free Proxies Safe? If you grab a server from our locations page to exit from a specific country, run the same before-and-after check. Common questions are answered in the FAQ.
Comments
Loading comments…
Leave a comment